Zimbra urges customers to patch critical web client XSS flaw
The Zimbra security team urged customers to patch a critical vulnerability affecting the Classic Web Client used to access the Zimbra Collaboration suite. [...]
Insights
Engineering perspectives on architecture, product development, AI, and the everyday decisions behind useful software.
From the engineering desk
Browse practical articles or follow the latest technology updates.
Subscribe via RSS →Curated links from external sources — not 360Softy original articles.
The Zimbra security team urged customers to patch a critical vulnerability affecting the Classic Web Client used to access the Zimbra Collaboration suite. [...]
Most enterprises assume their asset inventory is close enough to accurate. The evidence suggests otherwise. According to a survey of over 600 security leaders in the 2026 Axonius Actionability Report, only 45% of organizations consolidate their asset and exposure data into a single view, and every downstream security program inherits whatever the inventory gets wrong. Lumen Technologies, a
"I have been waiting a long time to finally get up there..."
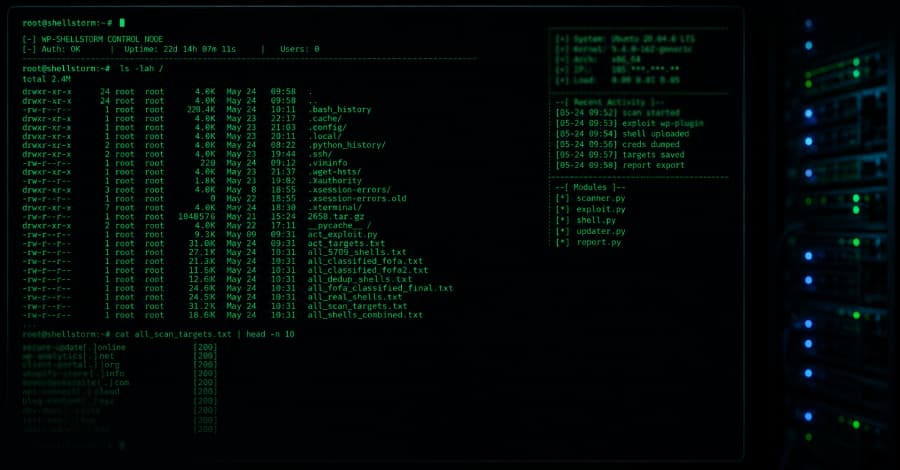
A cybercrime crew left one of its own servers wide open on the internet for three weeks, and it exposed the operation's inner workings: the hacking tools, the activity logs, and target lists naming more than 1.4 million websites. Far fewer were actually broken into, but the exposed files showed researchers how a mass site-hacking operation runs from the inside. The operation, now tracked as
The AC culture wars may be solved by advances in environmentally friendly technology.
The attackers call victims to direct them to phishing websites mirroring Microsoft Entra ID login pages. The post Okta Warns of Vishing Attacks Targeting Microsoft 365 Customers appeared first on SecurityWeek.
"We are delighted to actively help shape the ramp-up of the Ariane 6."
Let’s start with a conversation
An idea, a challenge, or a system that needs to work better. We’ll help you understand the next step.
Prefer email? [email protected]