Skip to content
HomeInsights

Insights

Ideas for building
better software.

Engineering perspectives on architecture, product development, AI, and the everyday decisions behind useful software.

From the engineering desk

Browse practical articles or follow the latest technology updates.

Subscribe via RSS →

Curated links from external sources — not 360Softy original articles.

ExternalCybersecurity
SecurityWeek

Obsidian Security Raises $85 Million at $1.1 Billion Valuation

Obsidian Security has developed a platform for governing AI agents across third-party applications. The post Obsidian Security Raises $85 Million at $1.1 Billion Valuation appeared first on SecurityWeek.

Application SecurityArtificial IntelligenceCybersecurity Funding
SecurityWeekRead original
External
The Hacker News

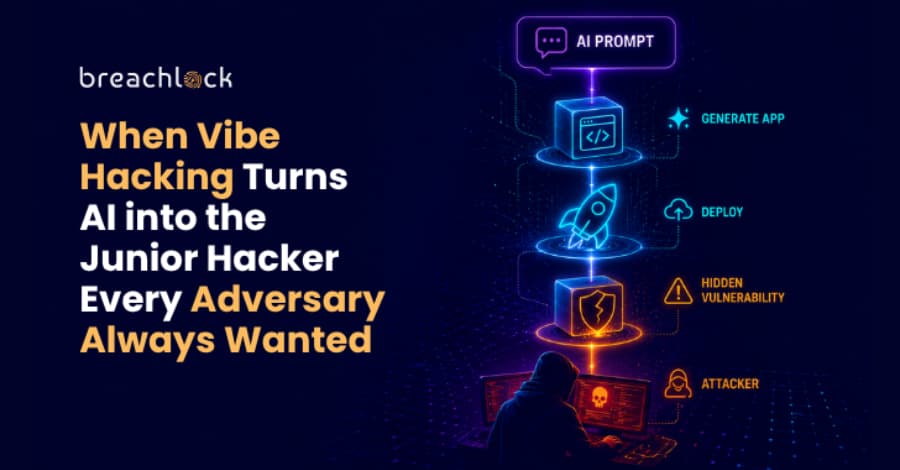
When Vibe Hacking Turns AI into the Junior Hacker Every Adversary Always Wanted

The cybersecurity industry has spent decades assuming that offensive capability scales with technical expertise. That assumption is starting to break. Security teams have long estimated risk by ranking attacker sophistication. Nation-state actors sat at one end. Organized criminal groups followed. Inexperienced attackers, dismissed as "script kiddies," sat at the other end, running public

The Hacker NewsRead original
External
The Hacker News

Google Deletes 3 ADK AI Workflows After Malicious GitHub Issue Could Trigger Privileged Agent

Google deleted three AI agent workflows from its Agent Development Kit (ADK) Python repository. Pillar Security showed that a public GitHub issue could manipulate a triage agent into triggering a privileged code-fixing agent. The researchers said the public agent could be prompt-injected into posting /adk-issue-fix as adk-bot. They identified the bot as a collaborator, so that comment satisfied

The Hacker NewsRead original
ExternalBackend Development
Django Weblog

Django security releases issued: 6.0.8 and 5.2.17

In accordance with our security release policy, the Django team is issuing releases for Django 6.0.8 and Django 5.2.17. These releases address the security issues detailed below. We encourage all users of Django to upgrade as soon as possible. CVE-2026-15307: Server-side file-write and request forgery via spatial lookups Spatial lookups allowed str and dict lookup values to be passed to GDALRaster when they represented rasters. Depending on the raster driver, this could write a file to disk (in

Django WeblogRead original

Let’s start with a conversation

Tell us what you’re working on.

An idea, a challenge, or a system that needs to work better. We’ll help you understand the next step.