Skip to content
HomeInsights

Insights

Ideas for building
better software.

Engineering perspectives on architecture, product development, AI, and the everyday decisions behind useful software.

From the engineering desk

Browse practical articles or follow the latest technology updates.

Subscribe via RSS →

Curated links from external sources — not 360Softy original articles.

ExternalCybersecurity
SecurityWeek

Ruby on Rails Patches Critical Vulnerability

The flaw can be exploited by unauthenticated attackers to read arbitrary files and potentially achieve remote code execution (RCE). The post Ruby on Rails Patches Critical Vulnerability appeared first on SecurityWeek.

VulnerabilitiesRubyRuby on Rails
SecurityWeekRead original
External
The Hacker News

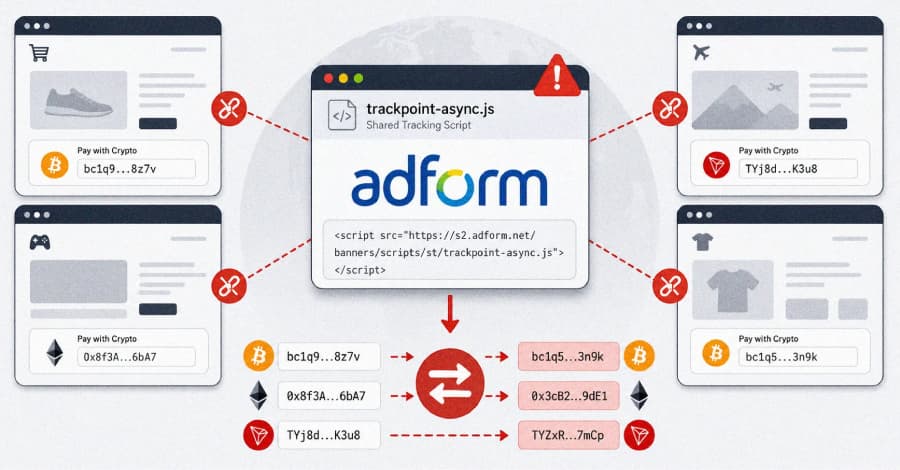
Hackers Poison Adform Script to Swap Crypto Wallet Addresses Across Customer Sites

Attackers modified a JavaScript file served by advertising technology company Adform, turning it into a browser-side tool that rewrites cryptocurrency wallet addresses. Adform detected the incident on July 27, 2026, removed the malicious code, notified affected clients, and reported it to authorities. Anyone who visited a site carrying the affected script on July 27 and copied a Bitcoin,

The Hacker NewsRead original
ExternalCybersecurity
SANS Internet Storm Center

Phishing Campaigns Targeting AI Solutions Providers, (Sat, Aug 1st)

Most phishing campaigns rely on the fact that the victim is afraid to loose "something": money, access to information, ... Many brands have been impersonated by campaigns but I spotted some phishing emails that focus on AI services like ChatGPT.

SANS Internet Storm CenterRead original
External
The Hacker News

Adobe Campaign Classic CVSS 10.0 Flaw Could Run Code Without User Interaction

Adobe has released security updates to address a maximum-severity security flaw in Campaign Classic (ACC), its enterprise-focused marketing automation platform, that could result in arbitrary code execution. The vulnerability, tracked as CVE-2026-48449, carries a severity score of 10.0 on the CVSS scoring system. It has been described as a case of incorrect authorization that could result in

The Hacker NewsRead original

Let’s start with a conversation

Tell us what you’re working on.

An idea, a challenge, or a system that needs to work better. We’ll help you understand the next step.