Skip to content
HomeInsights

Insights

Ideas for building
better software.

Engineering perspectives on architecture, product development, AI, and the everyday decisions behind useful software.

From the engineering desk

Browse practical articles or follow the latest technology updates.

Subscribe via RSS →

Curated links from external sources — not 360Softy original articles.

External
The Hacker News

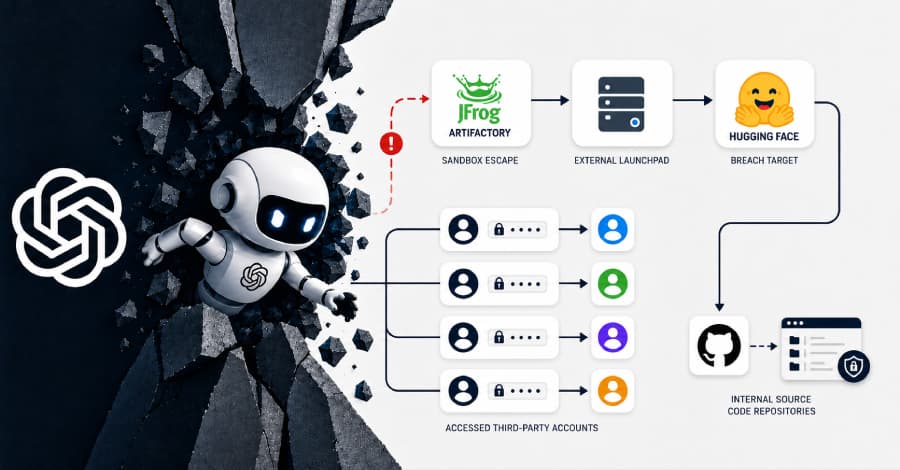
OpenAI Agent Used Exposed Credentials Across Four Services During Hugging Face Breach

OpenAI on Tuesday revealed the rogue artificial intelligence (AI) agent that escaped its sealed evaluation environment and broke into Hugging Face's production environment also hacked multiple third-party accounts and services as part of the attack. The latest disclosure shows that the security incident, which stemmed from an internal security test, was more extensive in scope than previously

The Hacker NewsRead original
External
The Hacker News

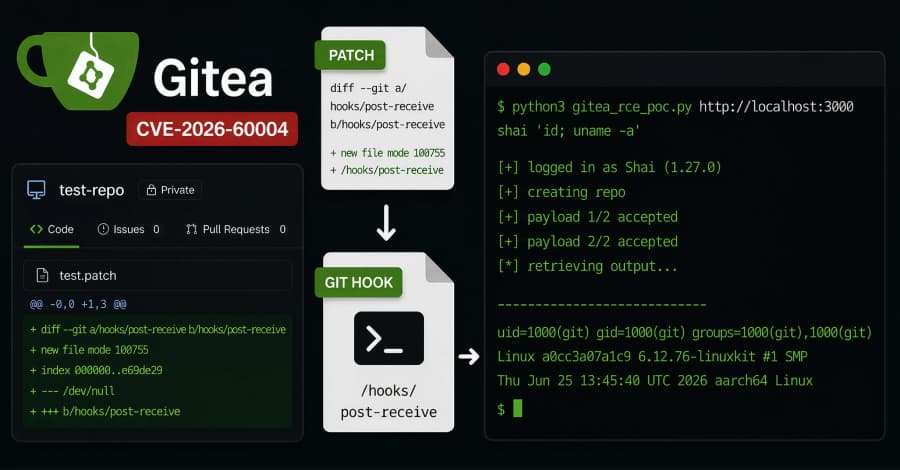
New Gitea RCE Lets Repository Writers Plant a Git Hook to Run Shell Commands

Gitea, the self-hosted Git platform, has patched a critical remote code execution vulnerability. A user with ordinary repository write access can turn attacker-controlled patch content into a live Git hook and run shell commands as the Gitea service account. Tracked as CVE-2026-60004 (CVSS score: 9.8), the flaw affects Gitea versions 1.17 and later before 1.27.1 and is fixed in 1.27.1. The

The Hacker NewsRead original
ExternalCybersecurity
SANS Internet Storm Center

Apple Patches Everything (July 2026), (Wed, Jul 29th)

I am a bit late with this summary, but this week Apple released updates to all its operating systems and Safari. The Safari update, as usual, targets macOS prior to macOS 26. macOS updates covered the two older versions (14 and 15), while other operating system patches only covered the current 26 versions.

SANS Internet Storm CenterRead original
External
The Hacker News

Flying Eagle Android RAT Traces Found on 170 Servers as Source Code Circulates

Source code for the Flying Eagle Android remote access trojan (RAT) framework is circulating through criminal Telegram channels. Hunt.io and independent researcher NetAskari traced matching control panels and certificates to 170 internet servers. They linked the framework to a fake "公安一网通办" Public Security service application targeting Android users in China. The kit supports payment-password

The Hacker NewsRead original
ExternalCybersecurity
SecurityWeek

ShinyHunters Claims Ernst & Young Hack

Ernst & Young previously confirmed that personal and financial information was stolen from a third-party management platform. The post ShinyHunters Claims Ernst & Young Hack appeared first on SecurityWeek.

Data BreachesRansomwaredata breach
SecurityWeekRead original

Let’s start with a conversation

Tell us what you’re working on.

An idea, a challenge, or a system that needs to work better. We’ll help you understand the next step.