Skip to content
HomeInsights

Insights

Ideas for building
better software.

Engineering perspectives on architecture, product development, AI, and the everyday decisions behind useful software.

From the engineering desk

Browse practical articles or follow the latest technology updates.

Subscribe via RSS →

Curated links from external sources — not 360Softy original articles.

ExternalCybersecurity
SecurityWeek

Critical SimpleHelp Vulnerability Exploited for Malware Delivery

The threat actor is focused on collecting credentials, SSH keys, cryptocurrency wallets, and development tooling. The post Critical SimpleHelp Vulnerability Exploited for Malware Delivery appeared first on SecurityWeek.

Malware & ThreatsVulnerabilitiesCISA KEV
SecurityWeekRead original
External
The Hacker News

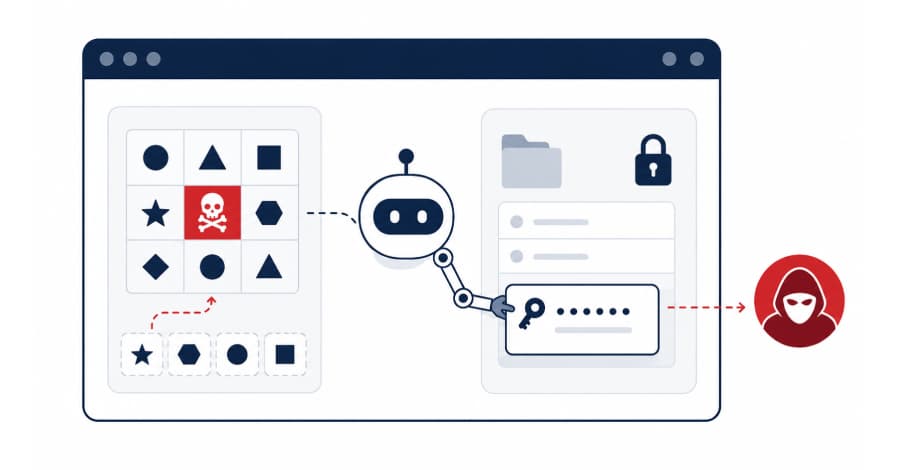
New BioShocking Attack Tricks AI Browsers Into Leaking User Credentials

Convince an AI browser that it is playing a game, and it can hand over your login details. That is the finding behind BioShocking, a technique from security firm LayerX that tricked six AI browsers and assistants into copying a user's credentials and sending them to an attacker. The targets included OpenAI's ChatGPT Atlas, Perplexity's Comet, and Anthropic's Claude browser extension. An

The Hacker NewsRead original
ExternalSoftware Engineering
GitHub Changelog

Per-user AI credit budgets available for cost centers

Enterprise admins can now set a cost center user-level budget: one per-user AI credit budget on a cost center that applies to every individual in it. As membership changes, the… The post Per-user AI credit budgets available for cost centers appeared first on The GitHub Blog.

GitHub ChangelogRead original
ExternalSoftware Engineering
Stack Overflow Blog

Why intent prediction needs more than an LLM​​​​‌‍​‍​‍‌‍‌​‍‌‍‍‌‌‍‌‌‍‍‌‌‍‍​‍​‍​‍‍​‍​‍‌​‌‍​‌‌‍‍‌‍‍‌‌‌​‌‍‌​‍‍‌‍‍‌‌‍​‍​‍​‍​​‍​‍‌‍‍​‌​‍‌‍‌‌‌‍‌‍​‍​‍​‍‍​‍​‍‌‍‍​‌‌​‌‌​‌​​‌​​‍‍​‍​‍‌‍​‌‍‌‌​​‍‍‌​‌‌​‌‍​‌‌‍​‌‍‍‌‍‌‌‍‌‍‌‌‌​‍‌‍‌‍‌‍​‌‍‌‌​‍‍‌‍​‌‍​‍‌‍‍‌‌‍‍‌‌​‌‍‌‌‌‍‍‌‌​​‍‌‍‌‌‌‍‌​‌‍‍‌‌‌​​‍‌‍‌‌‍‌‍‌​‌‍‌‌​‌‌​​‌​‍‌‍‌‌‌​‌‍‌‌‌‍‍‌‌​‌‍​‌‌‌​‌‍‍‌‌‍‌‍‍​‍‌‍‍‌‌‍‌​​‌​‌‌​​​‌‍‌‍​‌​​‌‌​​​​‍‌‌‍​​‍‌​‌​‌‍‌‍​‌‌​‌‌​‍‌​‌​‌‍‌‍​​‌​​‌​‍‌​‍​‌‍​‌‌‍‌​‌‍​​‍‌​‌‌​‌‌​‌‌​‌‍‌‍‌‌​‍​​​‍​​‌‌‍‌‌‌‍​‌​‌​‌​‍‌‌​‌‍‌‌​​‌‍‌‌​‌‌‍​‍‌‍​‌‍‌‍‌‌‌​​‌‍‌​‌‌​​‍‌​​‌‍​‌‌‌​‌‍‍​​‌‌‌​‌‍‍‌‌‌​‌‍​‌‍‌‌​‌‍​‍‌‍​‌‌​‌‍‌‌‌‌‌‌‌​‍‌‍​​‌‌‍‍​‌‌​‌‌​‌​​‌​​‍‌‌​​‌​​‌​‍‌‌​​‍‌​‌‍​‍‌‌​​‍‌​‌‍‌‍​‌‍‌‌​​‍‍‌​‌‌​‌‍​‌‌‍​‌‍‍‌‍‌‌‍‌‍‌‌‌​‍‌‍‌‍‌‍​‌‍‌‌​‍‍‌‍​‌‍​‍‌‍‌‍‍‌‌‍‌​​‌​‌‌​​​‌‍‌‍​‌​​‌‌​​​​‍‌‌‍​​‍‌​‌​‌‍‌‍​‌‌​‌‌​‍‌​‌​‌‍‌‍​​‌​​‌​‍‌​‍​‌‍​‌‌‍‌​‌‍​​‍‌​‌‌​‌‌​‌‌​‌‍‌‍‌‌​‍​​​‍​​‌‌‍‌‌‌‍​‌​‌​‌​‍‌‍‌‌​‌‍‌‌​​‌‍‌‌​‌‌‍​‍‌‍​‌‍‌‍‌‌‌​​‌‍‌​‌‌​​‍‌‍‌​​‌‍​‌‌‌​‌‍‍​​‌‌‌​‌‍‍‌‌‌​‌‍​‌‍‌‌​‍‌‍‌​​‌‍‌‌‌​‍‌​‌​​‌‍‌‌‌‍​‌‌​‌‍‍‌‌‌‍‌‍‌‌​‌‌​​‌‌‌‌‍​‍‌‍​‌‍‍‌‌​‌‍‍​‌‍‌‌‌‍‌​​‍​‍‌‌

Ryan sits down with Frank Portman, CTO at Yobi, to talk about why next-token prediction, though great for language, isn’t the right inductive bias for forecasting human behavior. They discuss how Yobi builds a “foundation model of behavior” using transformers and graph neural networks instead of chat-style LLMs, and what it takes to run millions of personalization decisions per second while keeping consumer data private.​​​​‌‍​‍​‍‌‍‌​‍‌‍‍‌‌‍‌‌‍‍‌‌‍‍​‍​‍​‍‍​‍​‍‌​‌‍​‌‌‍‍‌‍‍‌‌‌​‌‍‌​‍‍

podcastse-techse-stackoverflow
Stack Overflow BlogRead original
External
The Hacker News

Progress Kemp LoadMaster Flaw Could Let Attackers Run Root Commands Pre-Auth

A critical vulnerability in Progress Kemp LoadMaster can let an unauthenticated attacker execute arbitrary commands as root on the appliance by sending a crafted request to its API. The flaw, tracked as CVE-2026-8037, carries a CVSS score of 9.8 according to ZDI. A patch is available. If you run LoadMaster with the API enabled, update now. Progress published its advisory on June

The Hacker NewsRead original

Let’s start with a conversation

Tell us what you’re working on.

An idea, a challenge, or a system that needs to work better. We’ll help you understand the next step.