ExternalTechnology Trends
Hacker News
Kimi K3: Open Frontier Intelligence
Comments
Hacker NewsRead original
Insights
Engineering perspectives on architecture, product development, AI, and the everyday decisions behind useful software.
From the engineering desk
Browse practical articles or follow the latest technology updates.
Subscribe via RSS →Curated links from external sources — not 360Softy original articles.
Comments
Traditional security workflows were built for environments that changed at human speed. Token Security explains why AI agents require a new approach: building on a live identity foundation while giving security teams the flexibility to create workflows tailored to their own environments. [...]
We were building a DevOps agent to help with on-call remediation. The idea was straightforward: when an incident fires, the agent reads the relevant runbook from our internal wiki, assesses the situation, and executes the appropriate remediation steps. No waiting for an engineer to wake up at 3 am, find the right page, and manually run through a checklist. The agent had the context, the tools, and the access it needed to act. It needed elevated privileges to do the job. Restarting services, scal
Written by: Jules Czarniak Introduction As highlighted in the Mandiant M-Trends 2026 report, the mean time-to-exploit (TTE) has dropped to -7 days, meaning vulnerabilities are often exploited a week before a patch even exists. To keep pace, many security teams are exploring how to integrate large language model (LLM) agents into their codebases, development environments and continuous integration and continuous delivery (CI/CD) pipelines for automated vulnerability discovery and remediation.
Genetic testing company 23andMe has agreed to pay $18 million to settle claims from a coalition of 43 attorneys general that it failed to protect customers' genetic data. [...]
Comments
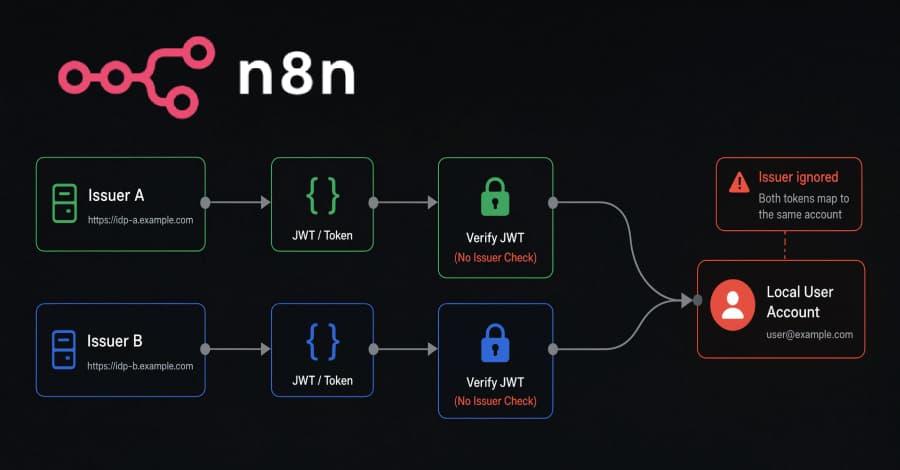
n8n, the workflow automation platform, handed out the wrong accounts at login. On Enterprise instances configured to trust more than one external token issuer, it matched an incoming JWT to a local user on the sub claim alone and ignored iss. A valid token from issuer A carrying a sub that belongs to someone under issuer B logged you in as them. Their password never
Comments
Let’s start with a conversation
An idea, a challenge, or a system that needs to work better. We’ll help you understand the next step.
Prefer email? [email protected]