Skip to content
HomeInsights

Insights

Ideas for building
better software.

Engineering perspectives on architecture, product development, AI, and the everyday decisions behind useful software.

From the engineering desk

Browse practical articles or follow the latest technology updates.

Subscribe via RSS →

Curated links from external sources — not 360Softy original articles.

ExternalObservability
Grafana Blog

Grafana 13.2 release: easier ways to query and explore your data

Grafana 13.2 is here, bringing more improvements to help you and your team explore your data and get to insights faster. In this post, we’ll highlight the latest updates to saved queries, a feature that lets teams share, discover, and reuse queries to get to trusted answers faster and help new teammates get up to speed. We’ll also explore how the new View panel sidebar makes exploring busy panels a breeze.  If you want to read about all the latest updates in Grafana 13.2, please refer to the ch

Grafana BlogRead original
ExternalCybersecurity
SANS Internet Storm Center

Using Microsoft Graph and Powershell to Mine for Information - Stale Accounts and Licenses, (Thu, Aug 20th)

Microsoft Graph is a newer API that is meant to replace several others.&#;x26;#;xc2;&#;x26;#;xa0; OK, it&#;x26;#;39;s at version 2.3.9, so it&#;x26;#;39;s not all that new, but it&#;x26;#;39;s new enough that lots of folks (and commercial tools) aren&#;x26;#;39;t using it yet.&#;x26;#;xc2;&#;x26;#;xa0; &#;x26;#;xc2;&#;x26;#;xa0;It allows you to Get and Set info from/to M365, Entra Users and Entra managed machines for starters.&#;x26;#;xc2;&#;x26;#;xa0; Let&#;x26;#;39;s dig in!

SANS Internet Storm CenterRead original
ExternalCybersecurity
SecurityWeek

MLflow Vulnerability Exploited for Cloud Credential Theft

The critical-severity flaw allows attackers to send HTTP requests to internal endpoints and extract sensitive information. The post MLflow Vulnerability Exploited for Cloud Credential Theft appeared first on SecurityWeek.

VulnerabilitiesexploitedMLflow
SecurityWeekRead original
External
The Hacker News

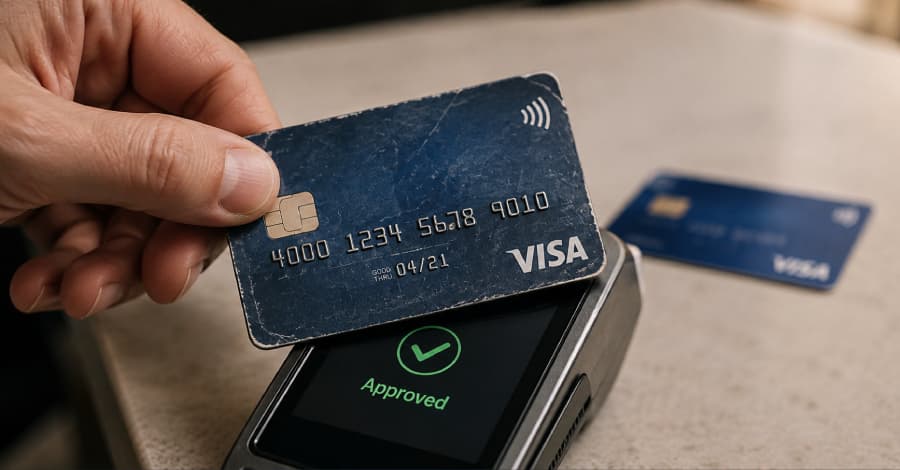
Zombie Card Attack Can Revive Expired Visa Cards for Contactless Payments

Researchers at the University of Massachusetts Amherst have demonstrated an attack that revives expired Visa contactless credit cards for real in-store purchases by rewriting the expiration date a point-of-sale (POS) terminal reads over near-field communication (NFC), without breaking any of the card's cryptography. The attack, which the researchers named "Zombie Card," requires physical

The Hacker NewsRead original

Let’s start with a conversation

Tell us what you’re working on.

An idea, a challenge, or a system that needs to work better. We’ll help you understand the next step.